Full installation of Team Password Manager on Ubuntu 26.04 with Apache
Current Team Password Manager version: 15.200.312This tutorial explains how to install Team Password Manager on a Linux Ubuntu 26.04 (LTS) system with the following components: Apache 2.4, MySQL 8.4, PHP 8.5 (with PHP-FPM), Sourceguardian Loader and a TLS/SSL certificate for https, either a commercial certificate or a free Let's Encrypt certificate.
Similar versions of this tutorial with lower versions of the components can be found here: Install on Ubuntu 18.04, Install on Ubuntu 20.04, Install on Ubuntu 22.04 and Install on Ubuntu 24.04.
A similar version of this tutorial with NGINX instead of Apache can be found here: Install on Ubuntu with NGINX.
To be able to follow this tutorial you'll need: a running Ubuntu 26.04 LTS system (preferably with nothing else installed), which can be accessed from anywhere on the Internet, root access to this system and a non-root user which we'll use to do everything with sudo for security. You'll also need some basic Linux knowledge.
- Basic settings
- Apache installation
- MySQL installation
- PHP installation
- Configuring the web server using Virtual hosts
- HTTPS and installing a commercial SSL Certificate
- HTTPS with a free Let's Encrypt certificate
- SourceGuardian Loader installation
- Team Password Manager database and user
- Team Password Manager files
- Team Password Manager configuration file
- Team Password Manager installation script
Basic settings
We'll be creating a Team Password Manager installation that will be accessed using this URL: https://tpm.mycompany.com. We'll be referring to this URL throughout this document, so adjust it to your own URL each time.
In this section we're going to prepare the system with some basic settings:
• Make sure the system is updated with the following commands:
$ sudo apt update && sudo apt upgrade
• Update the hosts file (/etc/hosts) with the hostname and the Team Password Manager URL. To do it:
1. Get the hostname of your computer with this command: $ hostname
2. Edit /etc/hosts and enter the following line:
IP ADDRESS hostname tpm.mycompany.com
If, for instance, the IP address ofyour server is 1.2.3.4 and your hostname is tpm-hostname, this line should be:
1.2.3.4 tpm-hostname tpm.mycompany.com
• Set the timezone of your server. Here we set it to UTC with the following command:
$ sudo timedatectl set-timezone UTC
See all the timezones you can use with: timedatectl list-timezones
Check with date:
Thu Oct 29 09:14:52 UTC 2026
• Enable the firewall (ufw), also enabling SSH through it. Execute these two commands to do it:
$ sudo ufw allow ssh
$ sudo ufw enable
• Make sure the server time is synced over the Internet. This is a must if you plan to use 2 factor authentication in Team Password Manager. Ubuntu 26.04 uses chrony for time synchronization, which is installed and enabled by default and uses Network Time Security (NTS) to authenticate the time servers. You can check that it's working with this command:
$ timedatectl
The output should include these two lines:
System clock synchronized: yes
              NTP service: active
You can also see the details of the synchronization (time source, offset, etc.) with: $ chronyc tracking
If chrony is not installed in your system (for example, in some minimal images), install it with: $ sudo apt install chrony
Note that there's no need to open any port in the firewall for this, as the server only makes outgoing requests to the time servers.
Apache 2.4 installation
We'll be using Apache 2.4 as our web server, from the Ubuntu 26.04 packages. To install it use the following command:
$ sudo apt install apache2
Once it's installed, enable http and https ports (80, 443) through the firewall:
$ sudo ufw allow in "Apache Full"
Set the server name globally in Apache. If you don't do it, Apache will show this warning each time it starts or checks its configuration: AH00558: apache2: Could not reliably determine the server's fully qualified domain name. To do it, create a configuration file with the ServerName directive (use your own subdomain instead of tpm.mycompany.com) and enable it:
$ echo "ServerName tpm.mycompany.com" | sudo tee /etc/apache2/conf-available/servername.conf
$ sudo a2enconf servername
$ sudo systemctl reload apache2
Since we'll be running PHP with PHP-FPM, we'll keep the default Apache MPM, which is event (unlike mod_php, PHP-FPM doesn't require MPM prefork). You can see it's the one in use with this command:
$ sudo apache2ctl -M | grep mpm
mpm_event_module (shared)
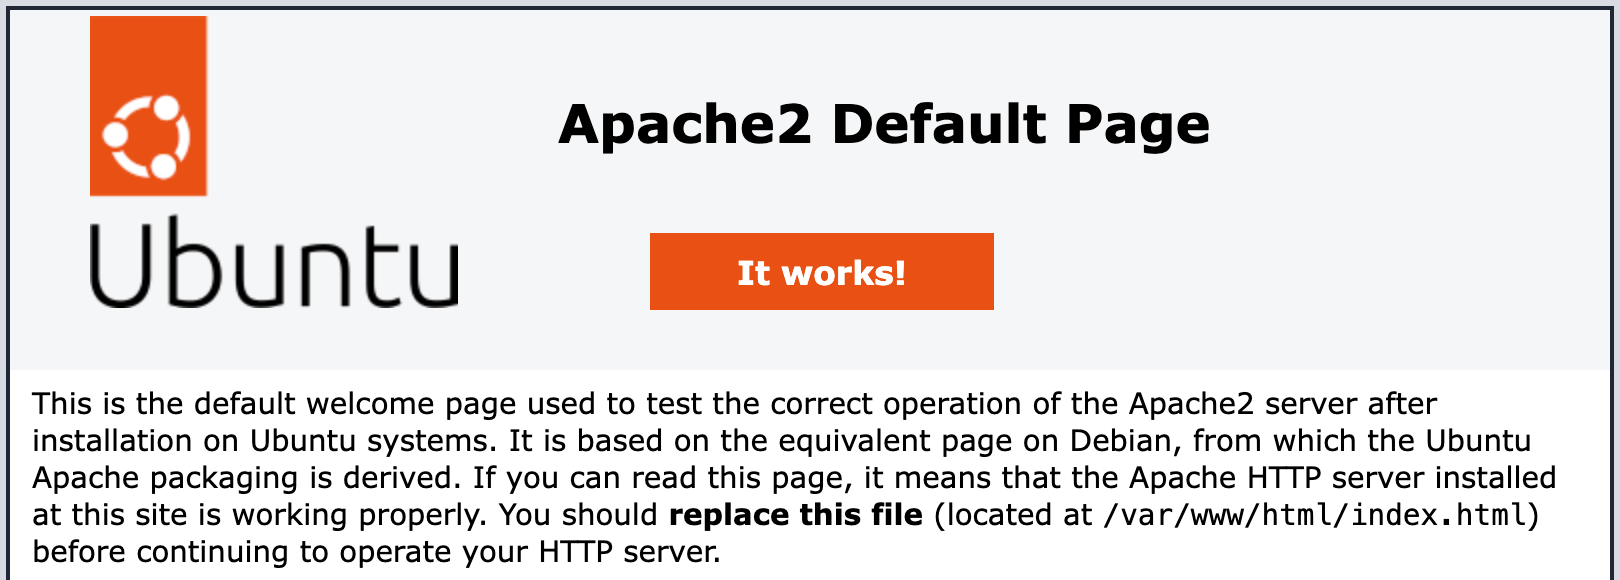
To test that Apache is running in your server you can open a web browser and type the IP address of your server in the address bar. If everything is ok you should see the following Apache default page:
MySQL 8.4 installation
We're going to use MySQL 8.4 (LTS) as the database for Team Password Manager. MySQL 8.4 is the default version of MySQL that installs with Ubuntu 26.04, so to install just use this command:
$ sudo apt install mysql-server
Once it's installed, run the security script to set the root password and some additional settings:
$ sudo mysql_secure_installation
You can safely set the following options in the script:
- Medium level of the password validation policy (Length >= 8, numeric, mixed case, and special characters).
- Remove anonymous users.
- Disallow root login remotely.
- Remove test database and access to it.
Once the script is finished you can test the connection using the following command:
$ sudo mysql
This will connect to the MySQL console using root because you're using sudo.
You'll be placed at the MySQL prompt: mysql>. Just type exit to return to the system prompt.
PHP 8.5 installation (PHP-FPM)
PHP 8.5 is the default version of PHP in Ubuntu 26.04, so we'll install it directly from the Ubuntu packages, without the need of any additional repository.
We'll run PHP using PHP-FPM (FastCGI Process Manager) instead of the Apache PHP module (mod_php). With PHP-FPM, PHP runs as a separate service (php8.5-fpm) and Apache passes the PHP requests to it. This allows Apache to use the more efficient MPM event and keeps PHP independent from the web server.
To install PHP-FPM and the modules that are required to run Team Password Manager, enter this command:
$ sudo apt install php8.5-fpm php8.5-common php8.5-cli php8.5-mysql php8.5-mbstring php8.5-ldap php8.5-curl php8.5-gd php8.5-xml
Check that you've installed the correct PHP version using this command: $ php -v. You should see an output similar to this one:
$ php -v
PHP 8.5.4 (cli) (built: Oct 19 2026 14:35:18) (NTS)
Copyright (c) The PHP Group
Built by Ubuntu
Zend Engine v4.5.4, Copyright (c) Zend Technologies
    with Zend OPcache v8.5.4, Copyright (c), by Zend Technologies
apt changelog php8.5lists each Ubuntu update and the CVEs it fixed.- Ubuntu’s CVE tracker shows the status of a given CVE per release.
The PHP-FPM service is started automatically after the installation. You can check its status with:
$ sudo systemctl status php8.5-fpm
Now let's tell Apache to pass the PHP requests to PHP-FPM. To do it, enable the Apache FastCGI proxy modules and the PHP-FPM configuration that the php8.5-fpm package has installed in Apache:
$ sudo a2enmod proxy_fcgi setenvif
$ sudo a2enconf php8.5-fpm
And restart Apache:
$ sudo systemctl restart apache2
Set PHP's timezone to match the one of your server's: edit /etc/php/8.5/fpm/php.ini (note that with PHP-FPM the php.ini file that's used is the one in the fpm folder) and set the following entry with the same timezone you set in the Basic settings section (all the PHP timezones can be found here: https://www.php.net/manual/en/timezones.php). In our case we set it to "UTC":
date.timezone = "UTC"
It's recommended to set expose_php = Off so that the PHP version is not exposed in headers, so go check it in php.ini and change it if it's set to On.
Oct 2026: PHP recommends setting session.upload_progress.enabled=0 until the next regular bugfix release. So just set this in /etc/php/8.5/fpm/php.ini too. To do it, search for the line with session.upload_progress.enabled, uncomment it if it's commented and set its value to 0 or Off.
After this, restart PHP-FPM:
$ sudo systemctl restart php8.5-fpm
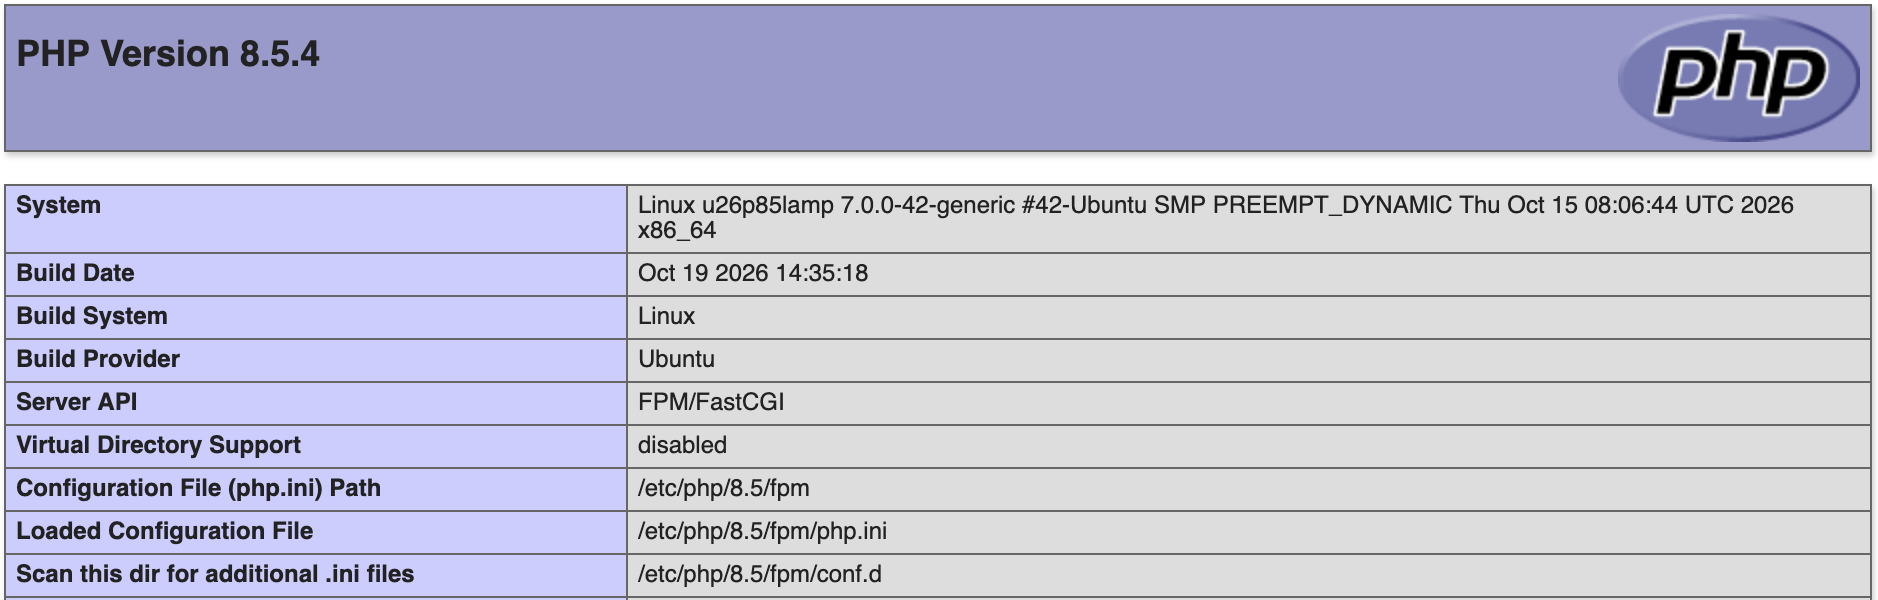
To check that PHP is correctly installed and communicating with Apache, do this:
1. Create a file called phpinfo.php in /var/www/html/ with the following content:
<?php phpinfo();
2. Open this file with the browser pointing at your IP address: http://IP_ADDRESS/phpinfo.php
You should see the phpinfo page with all the PHP settings. Note that the "Server API" entry shows "FPM/FastCGI", which means that PHP is being executed by PHP-FPM. You can send this to PDF to keep it for your records. Afterwards, delete the phpinfo.php file.
Configuring the web server to run our Team Password Manager installation using Virtual hosts
As stated earlier, we're going to access the Team Password Manager installation using this URL: https://tpm.mycompany.com. To make this possible, you need to do two things:
1. Create a new A/AAAA record in your DNS manager so that tpm.mycompany.com resolves to the server's IP address.
2. Configure a virtual host in Apache to accept tpm.mycompany.com (for port 80 (http) and 443 (https)) and make it execute the Team Password Manager installation.
Let's explain them in more detail:
1. Go to the DNS manager for your domain and create an A record (AAAA if IPv6) for your tpm.mycompany.com subdomain, specifying the IP address of your server and the default TTL value if you need to set one. To test open the browser and enter tpm.mycompany.com in the address bar. You should see the Apache default page. Note that this can take a while to propagate through all the DNS servers so it's normal if you don't see this immediately. Just wait for a few minutes.
2. Virtual hosts: virtual hosts allow your Apache server to serve more than one site and configure each site with their own set of options. In this case, "site" is the Team Password Manager installation. We'll configure one virtual host to serve tpm.mycompany.com. First we'll do the configuration for http://tpm.mycompany.com and later we'll configure https://tpm.mycompany.com with a commercial SSL certificate or a free Let's Encrypt one. Please follow these steps (remember always to change tpm.mycompany.com to your own subdomain):
2.1 Create a copy of the default Apache configuration file for the Team Password Manager site:
$ sudo cp /etc/apache2/sites-available/000-default.conf /etc/apache2/sites-available/tpm.mycompany.com.conf
2.2 Edit the tpm.mycompany.com.conf configuration file to look like this:
<Directory /var/www/html/tpm.mycompany.com/public_html>
	Require all granted
	AllowOverride All
	Options FollowSymLinks
</Directory>
<VirtualHost *:80>
	ServerName tpm.mycompany.com
	ServerAlias tpm.mycompany.com

	ServerAdmin info@mycompany.com

	DocumentRoot /var/www/html/tpm.mycompany.com/public_html

	ErrorLog /var/www/html/tpm.mycompany.com/logs/error.log
	CustomLog /var/www/html/tpm.mycompany.com/logs/access.log combined
</VirtualHost>
Some explanations:
/var/www/html/tpm.mycompany.com/public_htmlis where we'll put the Team Password Manager software files. We'll do this later on this tutorial. TheDocumentRootdirective is used to tell the web server that when a request is made to tpm.mycompany.com it should serve the files on /var/www/html/tpm.mycompany.com/public_html.- The
ErrorLogandCustomLogdirectives create specific logs for our installation, which are stored in/var/www/html/tpm.mycompany.com/logs/. Note that these logs are web server logs, not the internal log of Team Password Manager (which can be found in the top menu of the software, "Log" option). - We've also set the following options in the site folder:
Require all granted: all IP addresses can access the site,AllowOverride All: allows .htaccess files in folders to override the Apache configuration andOptions FollowSymLinksdisables directory listing for security.
2.3 Create the installation folders:
Execute this command to create the folders for Team Password Manager and logs:
$ sudo mkdir -p /var/www/html/tpm.mycompany.com/{public_html,logs}
public_html is the folder where we'll place the Team Password Manager files. logs is where the Apache logs will be written for our installation.
Both folders are currently owned by root, but it's better if you assign ownership to the Apache user and group, which for Ubuntu is www-data:
$ sudo chown -R www-data:www-data /var/www/html/tpm.mycompany.com
Then set appropriate permissions for public_html (read, write, execute for the Apache user and group, none for others):
$ sudo chmod -R 770 /var/www/html/tpm.mycompany.com/public_html
And the permissions for log (read, write, execute for the Apache user, read and execute for the Apache group, none others):
$ sudo chmod -R 750 /var/www/html/tpm.mycompany.com/logs
If you want your user to be able to create/edit files in public_html, you can add your user to www-data:
$ sudo usermod -aG www-data $USER
(you'll need to log out and log back in for this new group membership to apply)
Finally, ensure that new files and directories created within public_html and logs inherit the correct ownership and permissions by setting the setgid bit:
$ sudo chmod -R g+s /var/www/html/tpm.mycompany.com/public_html
$ sudo chmod -R g+s /var/www/html/tpm.mycompany.com/logs
The final result should be similar to this:
myuser@myhostname:/var/www/html/tpm.mycompany.com$ ls -la
total 16
drwxr-xr-x 4 www-data www-data 4096 Mar 11 12:42 .
drwxr-xr-x 3 root     root     4096 Mar 11 12:42 ..
drwxr-s--- 2 www-data www-data 4096 Mar 11 12:49 logs
drwxrws--- 7 www-data www-data 4096 Mar 11 19:29 public_html
2.4 Enable the site:
$ sudo a2ensite tpm.mycompany.com
Disable the default virtual host to minimize security risks:
$ sudo a2dissite 000-default.conf
And finally reload Apache:
$ sudo systemctl reload apache2
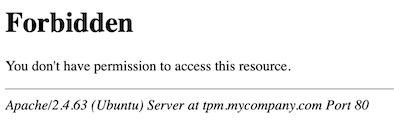
To test, enter http://tpm.mycompany.com/ in your browser and you should see this forbidden message as we haven't yet put any files in the public_html folder (and also due to Options FollowSymLinks):
Also, after accessing it, check the logs folder and you'll see the two log files: access.log and error.log.
HTTPS and installing an SSL Certificate from a Commercial Certificate Authority
Up to this point we've configured the server to accept requests to http://tpm.mycompany.com.
Note: if you prefer to use a free certificate from Let's Encrypt instead of a commercial one, skip this section and follow the next one: HTTPS with a free Let's Encrypt certificate. Use one or the other, not both.
In this section we'll:
- Install a commercial SSL certificate to avoid browser warnings about unsafe connections.
- Configure the web server to accept requests to https://tpm.mycompany.com (note the "s" in https), so that the communication between the client's browser and the server is encrypted.
Let's get to it. We'll first begin by changing to root user and updating the system:
$ su - root (and enter the root password)
# apt update && apt upgrade
To get a commercial SSL certificate we'll need a private key and a Certificate Signing Request (CSR) file. You can create them using the following commands:
Create a folder where to store the certificate files and go to that folder:
# mkdir /root/certs/ && cd /root/certs/
Execute openssl to create the private key and CSR (remember to use your own subdomain instead of tpm.mycompany.com):
# openssl req -new -newkey rsa:2048 -nodes -keyout tpm.mycompany.com.key -out tpm.mycompany.com.csr
When you execute this you'll be required to enter some information that will be integrated into your certificate request. It's specially important that you correctly enter the "Common name", which is the URL you want to use to access your installation of Team Password Manager. In this case we've used tpm.mycompany.com because we'll use https://tpm.mycompany.com to access our Team Password Manager installation (marked in red):
Generating a RSA private key
.....................+++++
......+++++
writing new private key to 'tpm.mycompany.com.key'
-----
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [AU]:ES
State or Province Name (full name) [Some-State]:Barcelona
Locality Name (eg, city) []:My city
Organization Name (eg, company) [Internet Widgits Pty Ltd]:My company
Organizational Unit Name (eg, section) []:Security
Common Name (e.g. server FQDN or YOUR name) []:tpm.mycompany.com
Email Address []:info@mycompany.com

Please enter the following 'extra' attributes
to be sent with your certificate request
A challenge password []:
An optional company name []:
The outcome of executing openssl are two files: tpm.mycompany.com.key and tpm.mycompany.com.csr.
tpm.mycompany.com.key is the private key, and you should protect it and not disclose it to anyone. tpm.mycompany.com.csr is the CSR file. You'll be required to copy and paste its contents into the online enrollment form when requesting the certificate.
You should now purchase the certificate from a Commercial Authority (CA). We've used Namecheap (PositiveSSL certificate) but you can use any CA that you like. The CA will ask you to copy the information in the CSR file (everything from -----BEGIN CERTIFICATE REQUEST to END CERTIFICATE REQUEST-----) and paste it on the indicated form. You can see the contents of the CSR file with this command: # cat tpm.mycompany.com.csr. You'll also need to validate your domain, the CA will provide various methods for doing so.
The CA will provide you with two files: tpm_mycompany_com.crt and tpm_mycompany_com.ca-bundle. Once you have them continue with the following steps:
Copy the files to the appropriate folders:
# cp tpm_mycompany_com.crt /etc/ssl/certs/
# cp tpm_mycompany_com.ca-bundle /etc/ssl/certs/

# cp tpm.mycompany.com.key /etc/ssl/private/
# cp tpm.mycompany.com.csr /etc/ssl/private/
Delete them from the /root/certs folder:
# rm /root/certs/tpm*
Note: we advise you to store all the certificate files outside the server, in a backup location.
The certificate files should be owned by root and protected by a permission setting of 600:
# chown root: /etc/ssl/private/tpm*
# chown root: /etc/ssl/certs/tpm*

# chmod 0600 /etc/ssl/private/tpm*
# chmod 0600 /etc/ssl/certs/tpm*
So the result of installing the certificate files should be something like this:
# ls -la /etc/ssl/certs/tpm*
-rw------- 1 root root 4135 Nov 10 15:24 /etc/ssl/certs/tpm_mycompany_com.ca-bundle
-rw------- 1 root root 2216 Nov 10 15:24 /etc/ssl/certs/tpm_mycompany_com.crt

# ls -la /etc/ssl/private/tpm*
-rw------- 1 root root 1102 Nov 10 15:24 /etc/ssl/private/tpm.mycompany.com.csr
-rw------- 1 root root 1704 Nov 10 15:24 /etc/ssl/private/tpm.mycompany.com.key
Let's now tackle the Apache configuration part.
Activate the ssl and headers modules:
# a2enmod ssl
# a2enmod headers
Restart Apache:
# systemctl restart apache2
We'll now edit the virtual host configuration file we created in the previous section (/etc/apache2/sites-available/tpm.mycompany.com.conf) to a) redirect http to https and 2) configure https. So edit this file to make it look like this, as always replacing tpm.mycompany.com with your own subdomain (we've marked the new lines in blue):
<Directory /var/www/html/tpm.mycompany.com/public_html>
	Require all granted
	AllowOverride All
	Options FollowSymLinks
</Directory>
<VirtualHost *:80>
	ServerName tpm.mycompany.com
	ServerAlias tpm.mycompany.com
	ServerAdmin info@mycompany.com
	DocumentRoot /var/www/html/tpm.mycompany.com/public_html

	ErrorLog /var/www/html/tpm.mycompany.com/logs/error.log
	CustomLog /var/www/html/tpm.mycompany.com/logs/access.log combined
	Redirect 301 / https://tpm.mycompany.com/
</VirtualHost>
<VirtualHost *:443>
    ServerAdmin info@mycompany.com
    ServerName tpm.mycompany.com
    ServerAlias tpm.mycompany.com

    DocumentRoot /var/www/html/tpm.mycompany.com/public_html
    ErrorLog /var/www/html/tpm.mycompany.com/logs/error.log
    CustomLog /var/www/html/tpm.mycompany.com/logs/access.log combined

    SSLEngine on

    SSLCertificateFile /etc/ssl/certs/tpm_mycompany_com.crt
    SSLCertificateKeyFile /etc/ssl/private/tpm.mycompany.com.key
    SSLCertificateChainFile /etc/ssl/certs/tpm_mycompany_com.ca-bundle

    # HSTS (mod_headers is required) (15768000 seconds = 6 months)
    Header always set Strict-Transport-Security "max-age=15768000"
</VirtualHost>
Let me explain some of the changes we've introduced:
- The
<VirtualHost *:80>section now has a new directive,Redirect, which we use to redirect the non encrypted requests (http) to the encrypted ones (https). So, even if a user goes to http://tpm.mycompany.com, she'll be automatically redirected to https://tpm.mycompany.com. - We've created a new section (
<VirtualHost *:443>) to configure https, to respond to requests made to https://tpm.mycompany.com. The information is the same of the non-ssl section but with the SSL directives.
Finally, reload Apache for the changes to take effect:
# systemctl reload apache2
You should also exit to get out of root return to the normal user.
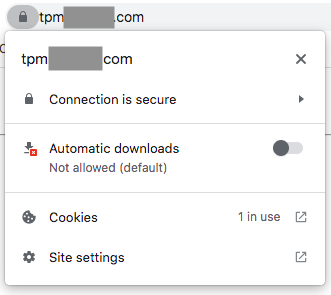
You can now test the requests: if you go to http://tpm.mycompany.com, you should be redirected to https://tpm.mycompany.com, and see the same forbidden message as before (as we still haven't installed the software files). This time, though, you can see that the browser shows you the secure connection "lock" icon and if you click on it you'll find information about the certificate:
HTTPS with a free Let's Encrypt certificate
This section is an alternative to the previous one: instead of purchasing a certificate from a commercial CA, we'll get a free certificate from Let's Encrypt using Certbot, which will also renew the certificate automatically before it expires. We'll configure Apache ourselves in the same virtual host file we already have, as we did with the commercial certificate. If you've already installed a commercial certificate in the previous section, skip this one.
Before starting, make sure that:
- tpm.mycompany.com resolves to the IP address of your server (the DNS record we created in the virtual hosts section). Let's Encrypt needs to reach your server through this name to validate it.
- Port 80 is open in the firewall (we did it with the "Apache Full" profile in the Apache installation section).
- The virtual host for tpm.mycompany.com is enabled and working on port 80, as we left it at the end of the virtual hosts section.
Install Certbot and its Apache plugin:
$ sudo apt install certbot python3-certbot-apache
Now request the certificate (remember to use your own subdomain instead of tpm.mycompany.com):
$ sudo certbot certonly --apache -d tpm.mycompany.com --deploy-hook "systemctl reload apache2"
Some explanations about this command:
certonlytells Certbot to only obtain the certificate and not to touch our Apache configuration (otherwise it would create a separate virtual host file for https).--apachetells Certbot to use Apache to validate that you control tpm.mycompany.com. It does it with a temporary configuration that's removed when the validation finishes.--deploy-hook "systemctl reload apache2"reloads Apache each time the certificate is renewed, so that it starts using the new one. Certbot remembers this setting for the automatic renewals.
The first time you run it, Certbot will ask you for an email address (optional) and to accept the Let's Encrypt terms of service. If everything went well you'll see a message like this one:
Successfully received certificate.
Certificate is saved at: /etc/letsencrypt/live/tpm.mycompany.com/fullchain.pem
Key is saved at:         /etc/letsencrypt/live/tpm.mycompany.com/privkey.pem
This certificate expires on 2027-01-27.
These files will be updated when the certificate renews.
Certbot has set up a scheduled task to automatically renew this certificate in the background.
The certificate files are stored in /etc/letsencrypt/live/tpm.mycompany.com/. fullchain.pem contains the certificate and the intermediate certificates (the equivalent of the .crt and .ca-bundle files of the commercial certificate) and privkey.pem is the private key. These are links to the latest version of the certificate, so we'll always use these paths in the Apache configuration.
Let's now tackle the Apache configuration part.
Activate the ssl and headers modules:
$ sudo a2enmod ssl headers
Restart Apache:
$ sudo systemctl restart apache2
We'll now edit the virtual host configuration file we created in the virtual hosts section (/etc/apache2/sites-available/tpm.mycompany.com.conf) to a) redirect http to https and b) configure https. So edit this file to make it look like this, as always replacing tpm.mycompany.com with your own subdomain (we've marked the new lines in blue):
<Directory /var/www/html/tpm.mycompany.com/public_html>
	Require all granted
	AllowOverride All
	Options FollowSymLinks
</Directory>
<VirtualHost *:80>
	ServerName tpm.mycompany.com
	ServerAlias tpm.mycompany.com
	ServerAdmin info@mycompany.com
	DocumentRoot /var/www/html/tpm.mycompany.com/public_html

	ErrorLog /var/www/html/tpm.mycompany.com/logs/error.log
	CustomLog /var/www/html/tpm.mycompany.com/logs/access.log combined
	Redirect 301 / https://tpm.mycompany.com/
</VirtualHost>
<VirtualHost *:443>
    ServerAdmin info@mycompany.com
    ServerName tpm.mycompany.com
    ServerAlias tpm.mycompany.com

    DocumentRoot /var/www/html/tpm.mycompany.com/public_html
    ErrorLog /var/www/html/tpm.mycompany.com/logs/error.log
    CustomLog /var/www/html/tpm.mycompany.com/logs/access.log combined

    SSLEngine on

    SSLCertificateFile /etc/letsencrypt/live/tpm.mycompany.com/fullchain.pem
    SSLCertificateKeyFile /etc/letsencrypt/live/tpm.mycompany.com/privkey.pem

    # HSTS (mod_headers is required) (15768000 seconds = 6 months)
    Header always set Strict-Transport-Security "max-age=15768000"
</VirtualHost>
This is the same configuration we used for the commercial certificate, except for the certificate files. Note that there's no SSLCertificateChainFile directive, as the intermediate certificates are already included in fullchain.pem.
Reload Apache for the changes to take effect:
$ sudo systemctl reload apache2
Let's Encrypt certificates are valid for 90 days. Certbot installs a systemd timer that renews them automatically when they're close to expiring, so you don't need to do anything. You can see the timer with this command:
$ systemctl list-timers | grep certbot
And you can test the renewal process (without actually renewing the certificate) with:
$ sudo certbot renew --dry-run
You can now test the requests: if you go to http://tpm.mycompany.com, you should be redirected to https://tpm.mycompany.com, and see the same forbidden message as before (as we still haven't installed the software files), with the browser showing the secure connection "lock" icon.
SourceGuardian Loader installation
Team Password Manager is a PHP web application encoded and secured using an encoder (SourceGuardian) and a loader is required to execute it. You need at least version 17.0.0 of the SourceGuardian Loader.
To install the Sourceguardian Loader follow these steps:
Go to https://www.sourceguardian.com/loaders.html and download the Linux x86_64 zip package. You should get the following file: loaders.linux-x86_64.zip.
Unzip it (it will create the "loaders.linux-x86_64" folder) and copy (or upload) the ixed.8.5.lin file into the following folder on your server: /usr/lib/php/20250925, which is the PHP 8.5 extensions folder, as you can see by running $ php -i | grep extension_dir.
Edit the PHP-FPM php.ini file in /etc/php/8.5/fpm/php.ini and put this line just below [PHP]:
extension=ixed.8.5.lin
Restart PHP-FPM:
$ sudo systemctl restart php8.5-fpm
To test: create a file called phpinfo.php in /var/www/html/tpm.mycompany.com/public_html with this content:
<?php phpinfo();
Open this file with the browser: https://tpm.mycompany.com/phpinfo.php
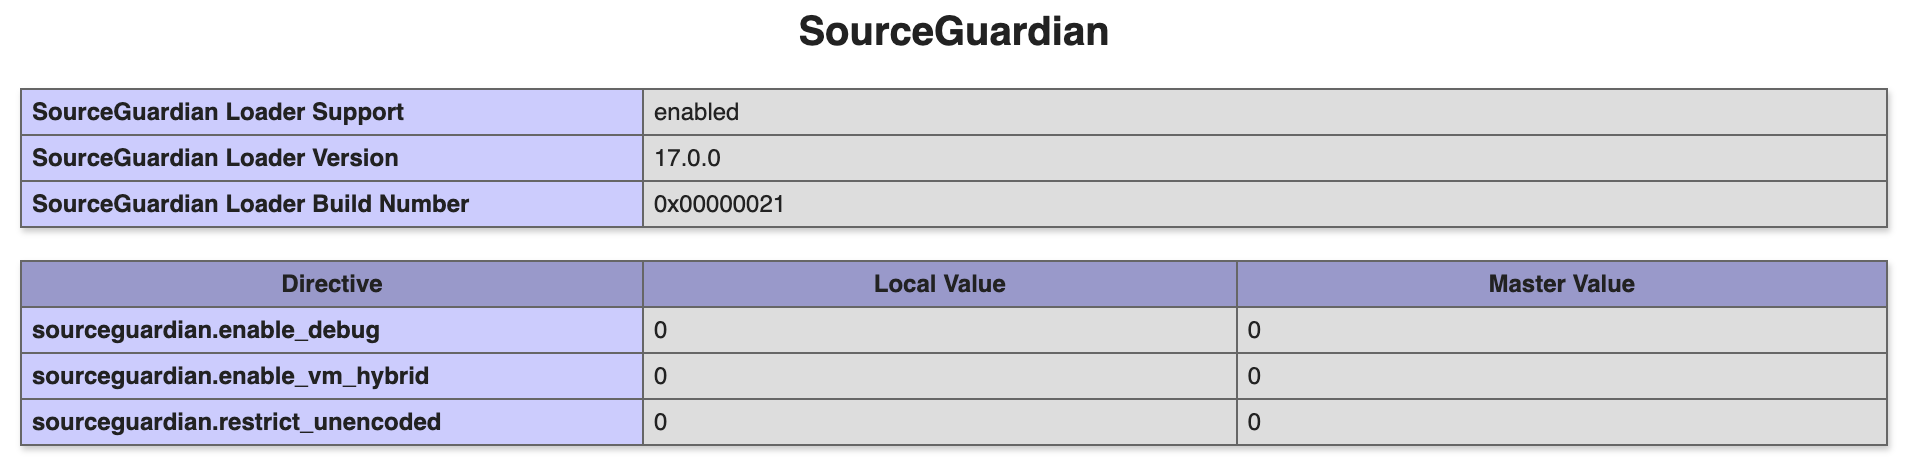
Check the "Sourceguardian" section, like in this image (note that for this tutorial the Loader version should be 17+):
Delete the phpinfo.php file.
Team Password Manager database and user
In this section we're going to create the database that will store the Team Password Manager information and a user to access this database from the software. We're going to use these values, we advise you use your own:
Database: tpm_database
User: tpm_user
Password: tpmPass%2026
Follow these steps to create the database and user:
1. Enter the mysql prompt. Since we're using sudo, we'll log in with the mysql root user:
$ sudo mysql
2. Type the following command at the mysql prompt to create the database:
mysql> CREATE DATABASE `tpm_database` CHARACTER SET utf8 COLLATE utf8_unicode_ci;
3. Type the following command at the mysql prompt to create the user:
mysql> CREATE USER 'tpm_user'@'%' IDENTIFIED BY 'tpmPass%2026';
3. Type the following commands at the mysql prompt to grant all the privileges to the user on the database:
mysql> GRANT ALL ON tpm_database.* TO 'tpm_user'@'%';
mysql> FLUSH PRIVILEGES;
Type exit at the mysql prompt to exit mysql and return to the normal linux prompt.
Team Password Manager files
Download the Team Password Manager software files from https://teampasswordmanager.com/download/, unzip the zip file and upload all the files and folders to /var/www/html/tpm.mycompany.com/public_html.
Let's now verify permissions. We're going to assign the following permissions to Team Password Manager files and folders: full to the user and group and none to the others (770):
$ chmod -R 770 *
You should have something like this when done. myuser is the user you're using to create the installation. Also note that at the time of writing this tutorial the version of Team Password Manager used is 15.200.312, so you might have different file sizes:
$ ls -la
drwxrws---  8 www-data www-data  4096 Nov 10 10:22 .
drwxr-xr-x  4 www-data www-data  4096 Nov 10 10:22 ..
-rwxrwx---  1 myuser   www-data  1873 Nov 10 10:22 config.php
drwxrws---  3 myuser   www-data  4096 Nov 10 10:22 css
-rwxrwx---  1 myuser   www-data  9475 Nov 10 10:22 eula.txt
-rwxrwx---  1 myuser   www-data   610 Nov 10 10:22 folder.php
drwxrws---  2 myuser   www-data  4096 Nov 10 10:22 import
-rwxrwx---  1 myuser   www-data 40544 Nov 10 10:22 index.php
-rwxrwx---  1 myuser   www-data 10180 Nov 10 10:22 install.txt
drwxrws---  2 myuser   www-data  4096 Nov 10 10:22 reports
-rwxrwx---  1 myuser   www-data    25 Nov 10 10:22 robots.txt
drwxrws---  8 myuser   www-data  4096 Nov 10 10:22 system
-rwxrwx---  1 myuser   www-data  5064 Nov 10 10:22 upgrade.txt
drwxrws---  2 myuser   www-data  4096 Nov 10 10:22 uploads
drwxrws--- 17 myuser   www-data  4096 Nov 10 10:22 wmm
Team Password Manager configuration file (config.php)
Edit the config.php file and enter the database, user and password configured in the database step:
// MySQL Database server
define('CONFIG_HOSTNAME', 'localhost');

// User that accesses the database server, that should have all privileges on the database CONFIG_DATABASE
define('CONFIG_USERNAME', 'tpm_user');

// User password
define('CONFIG_PASSWORD', 'tpmPass%2026');

// Database for Team Password Manager. You must manually create it before installing Team Password Manager
define('CONFIG_DATABASE', 'tpm_database');
As you can see, the database parameters in config.php are in clear text. Team Password Manager has the option of encrypting these parameters, so that if someone not authorized gets access to the config.php file, he won't be able to open the Team Password Manager database. You can see how this is done in the following document. You should do it after the installation is completed:
How to encrypt database parameters in config.php
Team Password Manager installation script
Open your browser and enter this in the address bar:
https://tpm.mycompany.com/index.php/install
You should see the Team Password Manager installation screen:
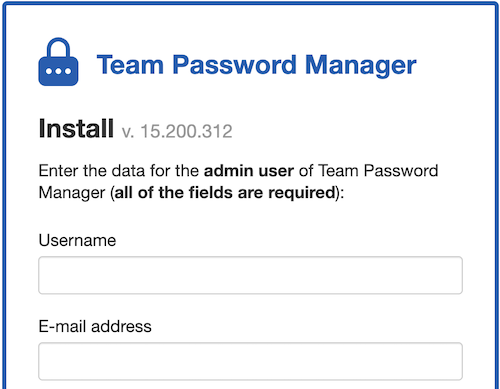
Just enter the values and complete the installation.
If everything went well Team Password Manager is now installed. Congratulations!!
Document changelog
| Nov 10, 2026: | Document updated to Ubuntu 26.04, PHP 8.5 with PHP-FPM, MySQL 8.4 and Let's Encrypt section. Previous version: Install on Ubuntu 24.04 |
| Sep 16, 2026: | Sourceguardian loader 17.0.0+ |
| Mar 12, 2025: | Document created, replacing the Ubuntu 22.04 one |
